Skip to content

Aembit Cloud configuration updates

Aembit Cloud corrects configuration workflows across Content Security, Client Workloads, Trust Providers, and authorization event reporting.

Key Updates:

  • Content Security tool lists: Switching between Allow and Block in a Content Security Provider keeps the tool list you configured, and Remove Tools clears the whole list in a separate step that asks you to confirm.
  • Redirect URI fields: A Redirect URI field on a Client Workload accepts a pasted value in every position, inserts a long pasted value rather than overwriting the text around it, and shows one validation message at a time. Copying the full contents of a field leaves the browser responsive.
  • Trust Provider secrets in custom Resource Sets: Terraform reads the state of a Trust Provider secret when that Trust Provider belongs to a custom Resource Set.
  • Authorization event timespan filters: The date filters on Access Authorization Events offer a maximum timespan of 24 hours, the window over which the Aembit Tenant UI makes authorization events available.
Google Cloud Identity-Aware Proxy (IAP) JWT Trust Provider now available

Aembit now offers a Google Cloud Identity-Aware Proxy (IAP) JWT Trust Provider. It validates the signed x-goog-iap-jwt-assertion token that IAP forwards to your workloads on Google Kubernetes Engine (GKE), Cloud Run, and App Engine after IAP authenticates a user.

Use this Trust Provider instead of the OIDC ID Token Trust Provider when IAP authenticates users in front of your workloads. IAP issues signed JWTs, but they aren’t standard OpenID Connect (OIDC) ID tokens. Google publishes the IAP signing keys at a static JWKS endpoint with no discovery document, and the audience identifies a Google Cloud resource rather than an OIDC client ID.

Aembit resolves Google’s signing key at validation time rather than from a preconfigured key set. It reads the key ID from the token, then retrieves the matching public key from Google’s IAP key endpoint. Aembit caches that key in memory, so your workload only forwards the token.

What’s new:

  • GCP IAP JWT Trust Provider type: Supply the IAP audience that identifies the Google Cloud resource IAP protects. Aembit pins the issuer and resolves the signing keys, so you don’t upload a key or enter a discovery URL.
  • Match rules on IAP token claims: Authorize on aud, iss, sub, and email, or on any additional claim IAP signs using custom_claim. The aud attribute supports wildcards, so one rule can cover more than one backend service in the same project.
  • Terraform support: Manage the Trust Provider through the Aembit Terraform provider with the aembit_trust_provider resource.

This Trust Provider validates the user identity that IAP asserts. To validate the identity of a workload running in Google Cloud, use the GCP Identity Token Trust Provider instead.

For the audience formats, match rule attributes, and configuration steps, see Google Cloud Identity-Aware Proxy (IAP) JWT Trust Provider.

AWS Application Load Balancer JWT Trust Provider now available

Aembit now offers an AWS Application Load Balancer JWT Trust Provider. It validates the signed x-amzn-oidc-data token that an AWS Application Load Balancer (ALB) forwards to your workloads after the ALB authenticates a user session with OpenID Connect (OIDC).

Use this Trust Provider instead of the OIDC ID Token Trust Provider when your workloads sit behind an ALB that authenticates users. ALB tokens require the AWS Application Load Balancer JWT Trust Provider.

Aembit resolves the signing key at validation time rather than from a preconfigured key set. It reads the AWS region and key ID from the token, validates the region before it contacts AWS, then retrieves and caches the matching regional public key. Aembit rotates those keys for you, so your workload only forwards the token.

What’s new:

  • AWS Application Load Balancer JWT Trust Provider type: Select the type and add your match rules. The type has no configuration fields of its own, so you don’t set a region or upload a signing key.
  • Match rules on ALB token claims: Authorize on aud, iss, sub, and email, or on any additional claim your identity provider forwards through the ALB using custom_claim. You can add more than one custom_claim rule to a single Trust Provider.
  • Terraform support: Manage the Trust Provider through the Aembit Terraform Provider with the aembit_trust_provider resource.

This Trust Provider works with Aembit Edge. Agent Controller support isn’t available yet.

For the match rule attributes, configuration steps, and troubleshooting, see AWS Application Load Balancer JWT Trust Provider.

Edge components release with Aembit CLI and Secrets Operator updates

Aembit has released new versions of the following components and packages:

  • Aembit Secrets Operator
  • Aembit Secrets Operator Helm chart

For the latest available versions of these components, see the Edge Components Supported Versions page.

Key Updates:

  • AWS and Kubernetes Trust Provider attestation in Aembit CLI: The aembit credentials get command now supports the AWS Metadata Service, AWS Role, and Kubernetes Service Account Trust Providers. Aembit CLI gathers attestation data from the local environment—instance metadata, an STS GetCallerIdentity request, or the projected service account token—so an externally supplied --id-token isn’t needed for these Trust Providers. The --deployment-model option now accepts vm, kubernetes, ecs_fargate, and lambda_container. The AWS Role Trust Provider requires this option.
  • Aembit Secrets Operator credential type support: Secrets Operator 1.32.322 now retrieves any credential type your Access Policy issues, not just HashiCorp Vault tokens. See Aembit Secrets Operator now supports more credential types.

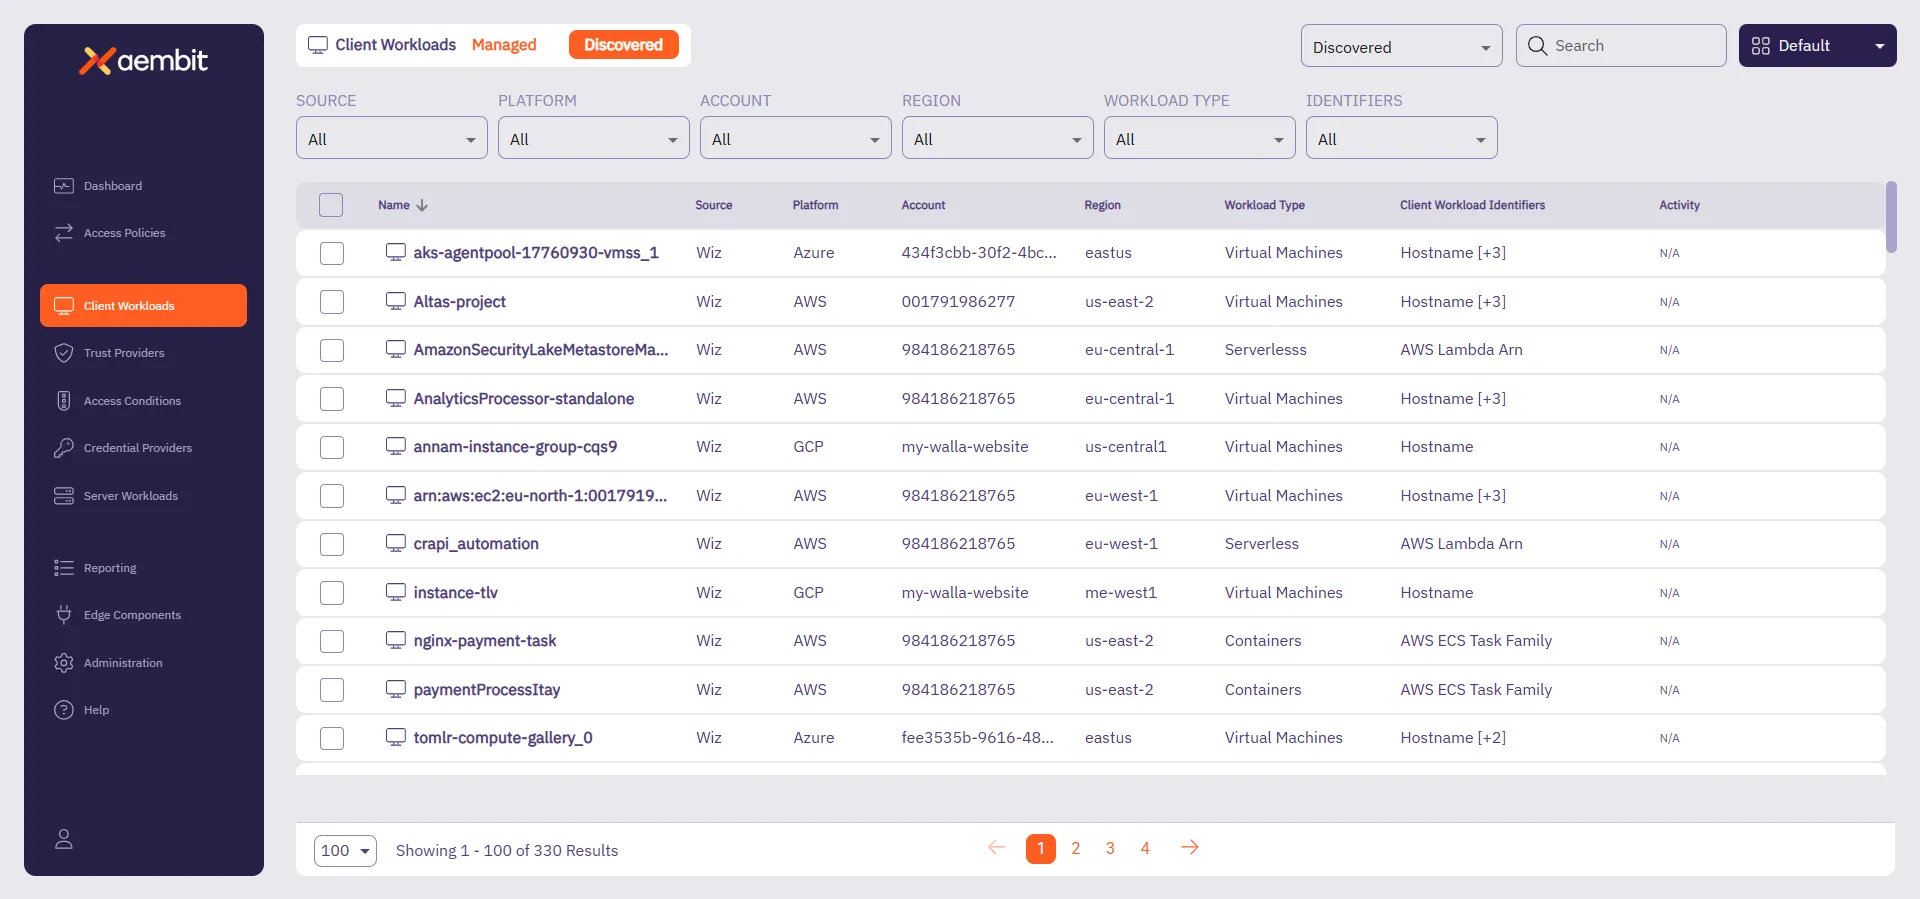
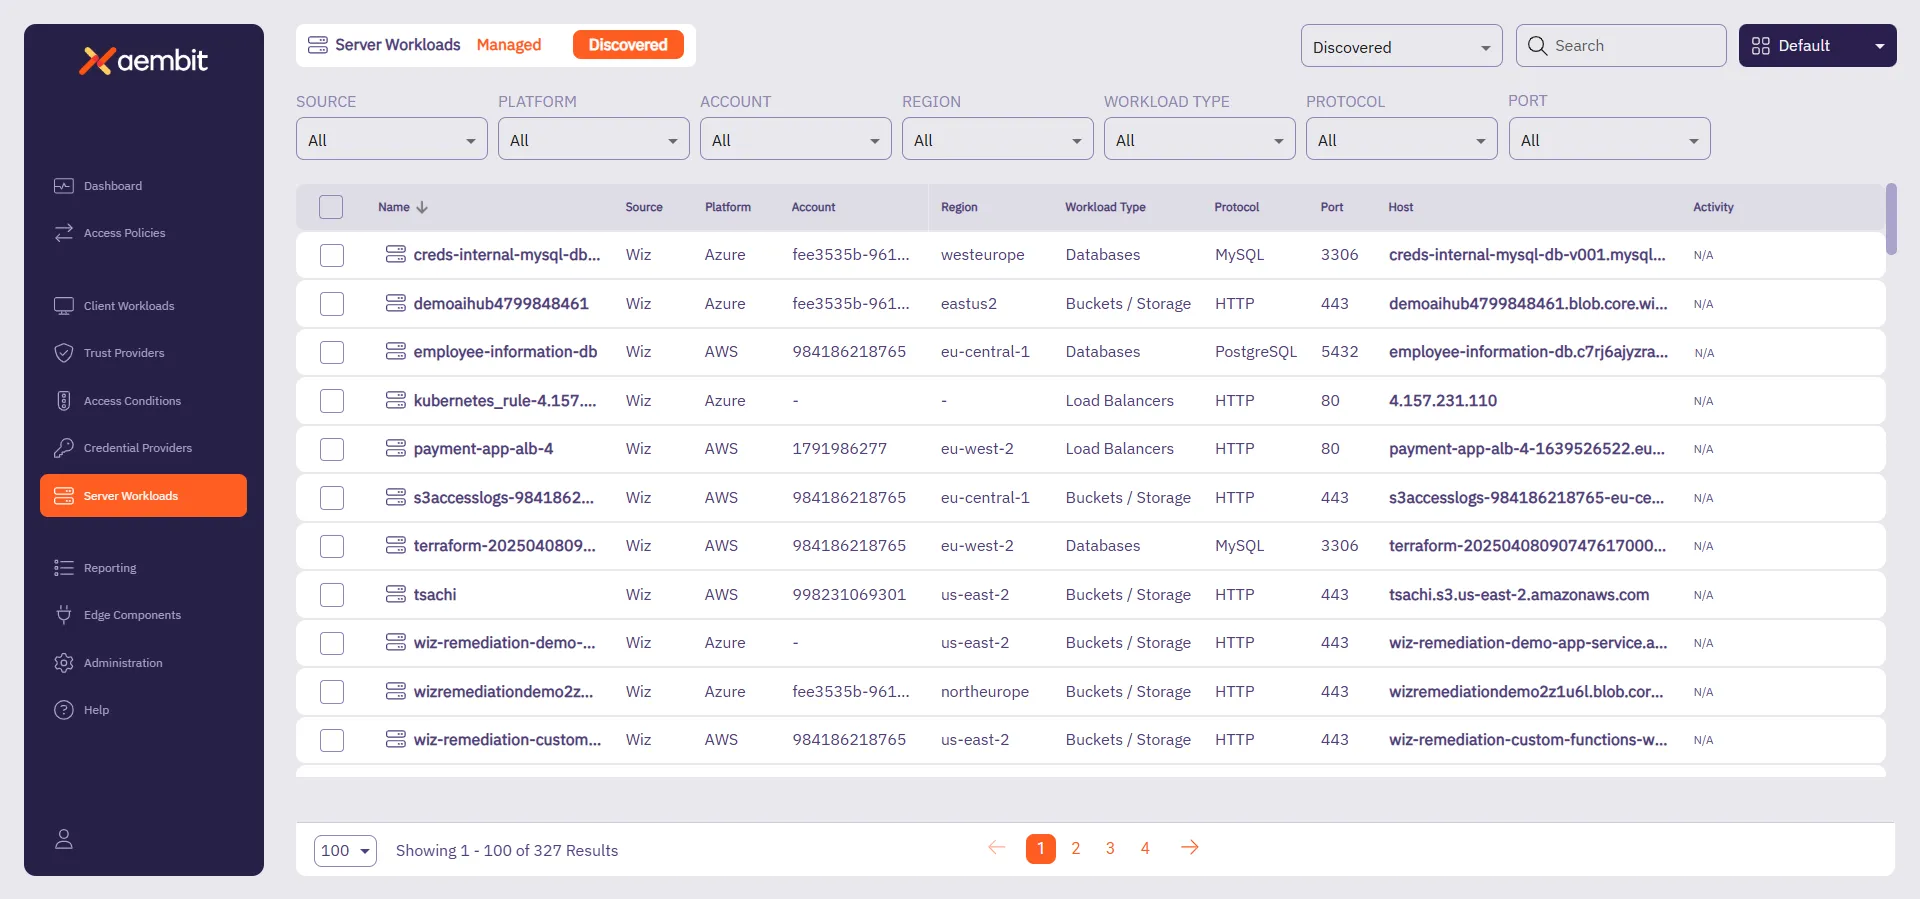
Discovery filtering and OIDC ID Token Trust Provider now available

Aembit has added more advanced filtering options to the Discovered tab for Client and Server Workloads. This enables you to find specific discovered workloads based on the criteria you filter.

Discovered Client Workloads page

Discovered Server Workloads page

See Filtering Discovered Workloads for more info.


Aembit has added the OIDC ID Token Trust Provider. This Trust Provider is Aembit’s solution for authenticating workloads using standard OIDC ID tokens. It validates incoming tokens against specific issuer, audience, and subject claims, giving you maximum flexibility to integrate with virtually any OIDC-compliant identity provider for secure, token-based workload access.

See OIDC ID Token Trust Provider for more info.


Aembit has applied security and performance enhancements to Agent Proxy version 1.24.3324 in this release.

Updated Edge Components:

  • Agent Proxy

Updated Edge Packages:

  • Helm Chart

  • Terraform ECS module

  • AWS Lambda Extension

See Edge Components supported versions for more details.

Vault private network access and CrowdStrike on Windows now available

Aembit now supports accessing HashiCorp Vault Credential Providers that reside on private networks. This allows your colocated Agent Proxy to handle authentication directly instead of Aembit Cloud. See Accessing Vault on private networks for more info.

Aembit now supports Conditional Access for CrowdStrike on Windows. To set up Conditional Access for CrowdStrike on Windows, follow the steps in Access Condition for CrowdStrike.

Aembit now supports the AWS Role Trust Provider on Agent Proxy for ECS Fargate deployments.

Enhanced Vault token header behavior.

Enhanced Agent Proxy initialization on Kubernetes to prevent other processes from interfering and impacting its startup.

Updated Edge Components:

  • Agent Proxy

Updated Edge Packages:

  • Helm Chart

  • Terraform ECS module

  • VM Agent Proxy package

  • AWS Lambda Extension

See Edge Components supported versions.

Multiple match rules of the same type now supported in Terraform Provider

The Aembit Terraform Provider is regularly updated with new features and capabilities to give you additional configuration options.

You may now use multiple Trust Provider match rules of the same type (OR-based combinations) in your Terraform Provider configuration.

For more detailed technical information on how to use similar match rule types in GitLab using the Aembit Terraform Provider, please see the Aembit Terraform Provider Registry technical documentation.

GitLab Jobs now supported in the Aembit Terraform Provider

The Aembit Terraform Provider is regularly updated with new features and capabilities to give you additional configuration options.

Aembit now supports both GitLab Job Client Identifiers and GitLab Job Trust Provider types, enabling you to manage Client Workloads in Gitlab using the Aembit Terraform Provider.

For more detailed technical information on how to manage Client Workloads in GitLab using the Aembit Terraform Provider, please see the Aembit Terraform Provider Registry technical documentation.

AWS Role Trust Provider now available

Aembit has released an update to support AWS Role-Based Trust Providers.

The ability to create and use different types of Trust Providers in your Aembit environment enables you to have flexibility in how resources are managed. With this enhancement, you now have an additional option when selecting a Trust Provider.

For more information on AWS Role-Based Trust Providers, please see the AWS Role Trust Provider page.

Kerberos Trust Provider now available for Active Directory

Aembit has released a Kerberos Trust Provider that enables the attestation of Client Workloads running in virtual machine environments joined to Active Directory. This attestation method is specifically designed for on-premise deployments where alternative attestation methods, such as AWS or Azure metadata service trust providers, are not available.

For more detailed information on this Kerberos Trust Provider, please refer to the Kerberos Trust Provider technical documentation.